With increased attacks on today’s enterprise systems, cybersecurity should be your ultimate business priority. Businesses are heavily relying on cloud platforms, remote work tools, mobile devices, and third-party software. While such technologies can encourage productivity, they might also extend the attack surface for cybercriminals. As per the recent landscape report, there is a 26% increase in total cyber-attack activity throughout the globe. Around 49% of attacks abuse legitimate tools.
However, there is no one-size-fits-all approach to application security. A fintech platform handling sensitive financial data might face different threats compared to an e-commerce website. This is why your business needs to understand the security testing methods that align with its industry. Well-planned security QA testing can help your organization assess vulnerabilities from multiple angles.
If you choose the right testing approach, it can enable your business to identify weaknesses before attackers can exploit them. From detecting coding flaws to assessing real-world attack scenarios, security tests can reduce risks.
What is Security Testing?
Security testing is a major inclusion when it comes to software testing, and it is focused on discovering security challenges and risks in software. It aims to keep your software protected from dangerous cyberattacks and data breaches, along with unauthorized access.
When it comes to security testing and identifying vulnerabilities, many leading businesses consider the expertise of a security QA testing company. Their process includes examining different areas of a system for security gaps, including authentication mechanisms, authorization controls, data protection, input validation, APIs, configurations, and network security. Depending on your testing method, security professionals might scan for known vulnerabilities while simulating real-world attack conditions. They might also investigate potential weaknesses while automating the tools they miss.
General software testing mainly prioritizes whether an application works as expected. On the other hand, security testing asks a different set of questions, like: can someone access information they should not see? Can attackers manipulate the software? Etc. Security testing also evaluates whether the same feature can be bypassed through techniques like injection attacks, weak credentials, or session manipulation.
You need to remember that security testing should also not be treated as your final checkpoint before the deployment process. This should be implemented throughout your software development journey. This approach can help your team identify security challenges during planning, development, testing, and deployment. You can easily fix vulnerabilities earlier while reducing expenses.
Key Security Testing Types Businesses Should Consider
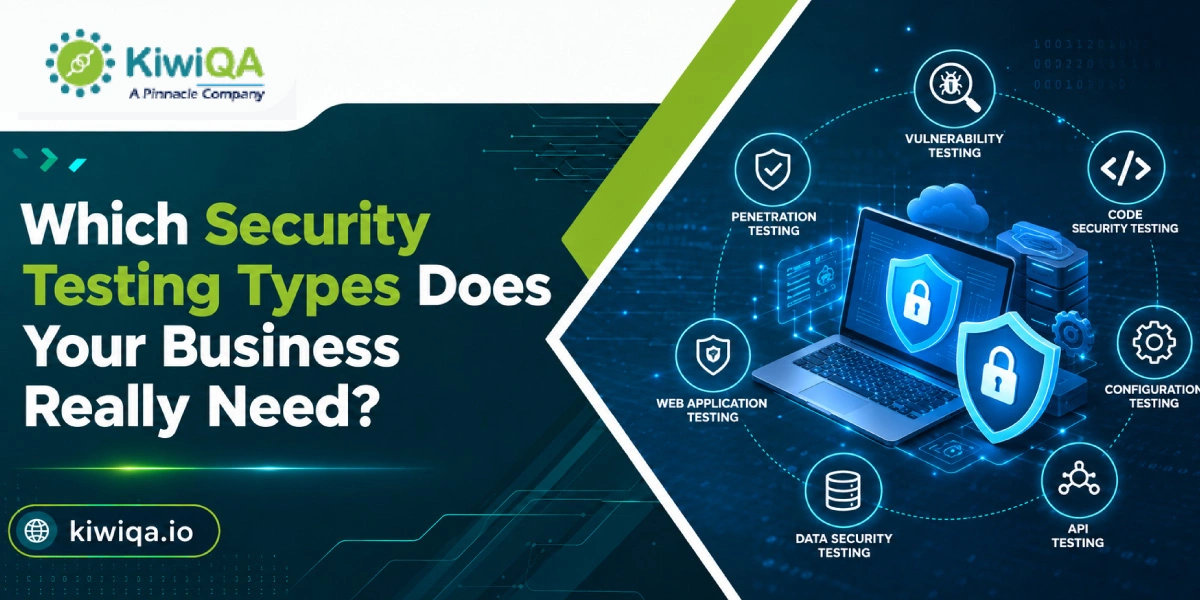
Different types of security testing are a must, as multiple applications, infrastructure, and business environments face different security challenges. Therefore, picking the right combination of security testing methods is necessary for creating a stronger security posture. Here are ten important types that you should be considerate of.
➥ Vulnerability Assessment
A vulnerability assessment is capable of verifying security weaknesses across your digital assets, including networks and applications. It generally uses systematic scans and analysis to verify issues like missing patches, outdated software, insecure configurations, and publicly known vulnerabilities.
The outcomes can help you understand the security exposure while prioritizing the weaknesses based on their severity and potential business impact. As new vulnerabilities continue to emerge, this type of assessment is generally suitable for regular security reviews. By approaching vulnerability assessment, you can easily address your risks early while maintaining better visibility into your overall security posture.
➥ Penetration Testing
Penetration testing is not just limited to identifying risks; it includes real-world scenarios to assess if security weaknesses can actually be exploited. In this process, a professional QA security testing company attempts to breach systems using similar techniques used by attackers. It can help you assess the real and exact influence of active risks present.
It will also check the effectiveness and strength of your recent security controls, including authentication mechanisms.
Penetration testing is highly valuable before major product launches and infrastructure upgrades, as it offers a practical assessment of how well an organization can tackle real potential attacks.
➥ Web Application Security Testing
This testing method verifies websites and web-based applications for vulnerabilities that could expose systems, users, or sensitive information to attacks. It assesses critical areas like session management, authentication processes, access controls, input handling, and application configurations.
The following testing can discover issues like injection vulnerabilities, insecure configurations, broken access controls, and other weaknesses commonly related to OWASP security risks. As web applications are generally exposed to the internet, even a small risk can create a major business impact. So, regular and continuous testing can help your industry understand the issues before they become accessible to attackers.
➥ API Security Testing
API security testing prioritizes preventing vulnerabilities in the interfaces that enable communication between applications, services, and platforms. It verifies authentication and authorization mechanisms to ensure that only real users are able to access your resources.
Testing also helps identify accidentally exposed sensitive data and ineffective access controls that could allow attackers to manipulate requests or access unauthorized information. As modern software is largely dependent on interconnected services, APIs have become a major attack surface. So, API testing is one such security testing type you should consider to reduce risks across the broader application ecosystem.
➥ Mobile Application Security Testing
This testing identifies vulnerabilities that affect Android and iOS applications and the systems they interact with. It verifies how sensitive data is stored on devices and whether communication between the application, APIs, and backend services is properly secured.
The process also examines user permissions and potential weaknesses that could expose application functionality or data. As mobile applications generally depend on backend APIs and third-party services, testing such integrations is necessary. A detailed assessment can help your business address risks across both the mobile applications and their connected infrastructure before security issues affect users.
➥ Network Security Testing
Network security testing assesses both internal and external networks to identify weaknesses that might give rise to unauthorized access. It verifies vulnerable ports, insecure services, exposed devices, and other entry points that attackers might attempt to exploit.
The following process also reviews firewall rules, network segmentation, and configurations to determine whether existing security controls offer better protection. Effective testing can also reveal unnecessary exposure and misconfigurations that might go unnoticed. As part of broader security testing services, network security assessment can help your organization strengthen its infrastructure while minimizing the chances of attackers gaining control of sensitive resources.
➥ Cloud Security Testing
Cloud security testing is responsible for evaluating cloud infrastructure, services, and configurations to identify risks that could expose your sensitive data. It verifies excessive permissions, access controls, and weak identity. It also assesses other configuration issues that might give users more access than necessary.
Testing also reviews data storage practices, encryption controls, and security testing to ensure critical information is properly protected.
As organizations increasingly operate across Microsoft Azure, AWS, and Google Cloud environments, understanding the security responsibilities within each deployment is necessary. Cloud security testing can help your business identify configuration and access-related weaknesses before they give rise to data exposure and security incidents.
➥ Security Configuration Testing
This testing approach is one of the major ones among different types of security testing. It focuses on identifying weaknesses caused by improperly configured systems, databases, applications, and infrastructure. Even well-developed software can become vulnerable when security settings are improperly integrated.
This testing reviews access permissions, default configurations, security policies, and system settings. This can help you identify unnecessary exposure. It can also detect unused services and features that should be disabled but remain active. By identifying and correcting the issues, your business can easily reduce avoidable risks and ensure the technology environment values established security best practices.
➥ Authentication and Authorization Testing
Authentication and authorization testing is a type of security testing that evaluates whether an application properly verifies user identities and restricts access as per defined permissions. It verifies login mechanisms and structures the verification process for finding defects that could allow an attacker to bypass the security controls.
The assessment also examines role-based access controls to ensure users can only access resources related to their responsibilities. Apart from this, it identifies privilege escalation risks where a standard user might gain higher-level permissions through misconfigurations. Effective authentication and authorization testing is needed to prevent unauthorized access and protect sensitive information. You can also be assured of the safety of your high-value business resources with this testing.
➥ Compliance Security Testing
Compliance security testing assesses whether an organization’s security controls align with applicable regulatory and industry needs. Depending on the business and the data it handles, this might include standards like PCI DSS, HIPAA, GDPR, and ISO 27001.
The testing process mainly identifies compliance-related security gaps, including weak access controls or missing safeguards.
Addressing such issues can help your business reduce regulatory risks while strengthening the overall security structure. Compliance testing can also help your organization prepare for internal and external audits by assessing potential gaps early while offering clearer visibility into whether required security controls are properly implemented.
Which Security Testing Types Does Your Business Actually Need?
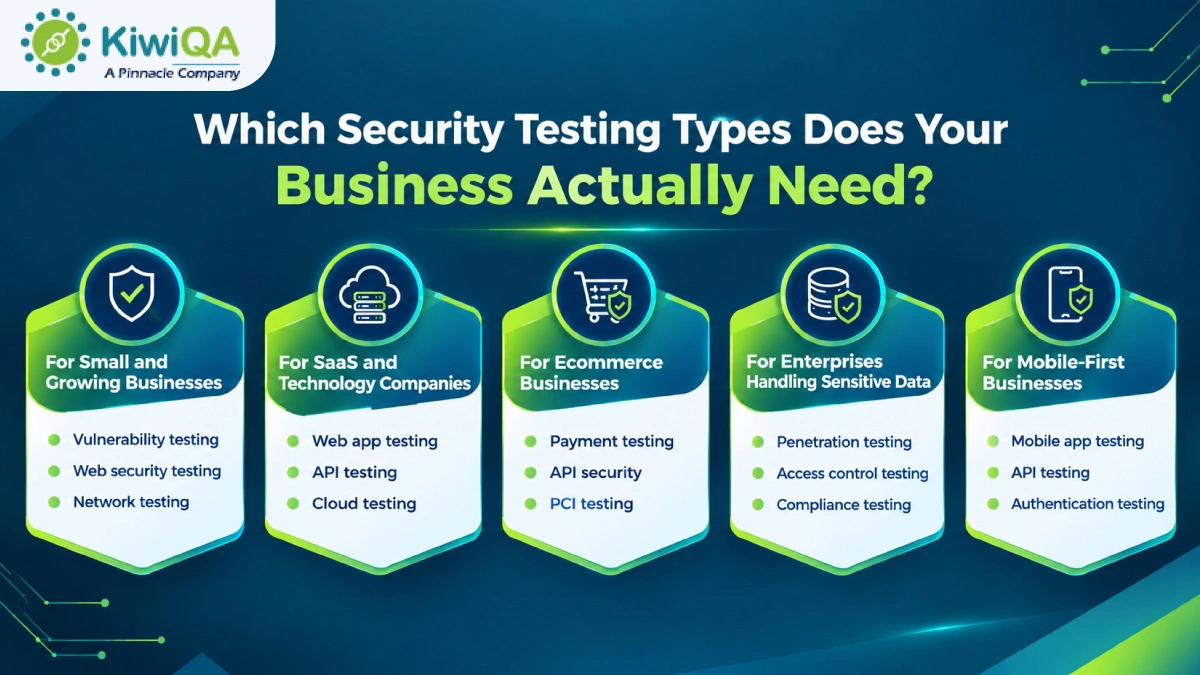
The right security testing strategy mainly depends on your business model, technology stack, and the type of data you handle, along with your risk exposure. While some companies desire continuous security assessment, others can start with targeted testing focused on their most critical assets.
➥ For Small and Growing Businesses
Small and growing businesses should form a strong security foundation without unnecessarily overloading their testing efforts. Regular vulnerability assessments can help you identify known weaknesses, while web application security testing can protect your customer-facing websites and apps. Network security testing is equally necessary for identifying exposed services, insecure configurations, and vulnerable devices within the business infrastructure.
Basic penetration testing can further validate whether critical vulnerabilities are actually exploitable. This combination offers smaller organizations practical visibility into their security risks while helping them address important risks before the digital infrastructure starts growing.
➥ For SaaS and Technology Companies
SaaS and technology firms generally operate within interconnected environments. This makes application and infrastructure security very important for you. Web application security testing can help identify vulnerabilities in customer-facing platforms, whereas API security testing protects the connections between applications, services, and third-party integrations.
Cloud security testing is necessary for identifying configuration mistakes and data protection risks within your cloud environment. Similarly, penetration testing offers a practical assessment of exploitable issues, while authentication and authorization testing ensures users can’t access resources beyond their assigned permissions. Together, such testing approaches can help your SaaS business protect customer data and maintain trust.
➥ For Ecommerce Businesses
Ecommerce businesses mainly handle customer accounts, transactions, personal information, and payment-related data. This creates multiple potential security risks. In such an environment, web application security testing can help you protect your online stores from common application breaches. API security testing secures connections between payment gateways, inventory systems, and other integrated services.
Payment security testing focuses on protecting transaction processes and sensitive financial data. Penetration testing can easily identify exploitable weaknesses across the broader ecommerce environment. In addition to this, PCI DSS compliance testing is generally necessary for businesses handling cardholder data. Combining such assessments can help ecommerce companies reduce fraudulent activities and data exposure that can easily affect customer trust.
➥ For Enterprises Handling Sensitive Data
Enterprises handling sensitive customer and confidential business data need a more comprehensive security testing approach. In such a scenario, a security QA testing company might consider penetration testing that helps evaluate whether attackers can exploit weaknesses across critical systems and applications.
Network security testing identifies risks within internal and external infrastructure, while cloud security testing addresses configuration, access, and data protection concerns in cloud environments. Access control testing ensures employees and users can only reach authorized resources, reducing the risk of privilege misuse. Mainly, compliance security testing can further help your organization identify gaps against applicable regulatory and industry needs while strengthening its overall security structure.
➥ For Mobile-First Businesses
Mobile-first businesses should secure their application and the whole infrastructure at the same time. Mobile application security testing helps identify vulnerabilities specific to Android and iOS applications, including insecure local storage, unsafe communication, and weak permissions. API security testing is necessary because mobile applications frequently exchange data with backend services through APIs.
Authentication testing can evaluate whether login and identity verification mechanisms can resist unauthorized access. Backend infrastructure testing further examines the servers, cloud services, databases, and configuration supporting the application. Together, such types of security testing can help your mobile-first business protect users and reduce risks across the whole mobile ecosystem.
Also Read : Security Testing in Retail App: Safeguarding Customer Data
How to Choose the Right Security Testing Approach?
Choosing the right security testing types is not just about applying every available testing method to every system. A more effective strategy is to assess where your business is most exposed and focus testing efforts accordingly. Your risk profile, compliance obligations, environment, and critical business factors should also influence the scope, as mentioned here.
➥ Evaluate Your Business Risk
Start by assessing the type of data your organization gathers and processes. You might face greater consequences if your business deals with financial details, personal information, or confidential business records. You should also consider the value of systems that might attract cyber attackers. Make sure to assess the potential influence of a security incident, including financial loss, legal consequences, operational disruption, and loss of customer trust. This risk assessment can help you determine which risks need the highest level of attention.
➥ Consider Your Technology Environment
Your security testing approach should match the tech environment your business operates within. Web applications need testing for common application vulnerabilities, while mobile applications need assessment focused on device-specific risks and local data storage. Your APIs should be tested carefully as they often connect multiple applications and services while handling sensitive data.
Businesses using cloud infrastructure must assess configurations, permissions, and data protection measures. Internal networks also need attention to identify exposed devices and configuration weaknesses. Mapping such environments can help you ensure that important attack surfaces are not ignored at all.
➥ Understand Your Compliance Requirements
Security testing decisions should also consider the compliance needs applicable to your industry and operations. Industry-specific regulations might require your business to implement particular security controls or conduct assessments at defined intervals. Data privacy regulations generate additional responsibilities around how personal and sensitive data is gathered, stored, accessed, and protected.
Understanding such factors can help your business choose security testing methods that address both genuine security risks and potential compliance gaps before they lead to penalties and audit issues.
➥ Prioritize Business-Critical Systems
Your business should prioritize testing for systems where a successful attack would have the greatest influence. Your customer-facing software needs immediate attention as it is directly exposed to external threats and often processes sensitive user data.
Payment platforms should be thoroughly assessed because of the financial data and transactions they manage. Business-critical databases containing customer, financial, or operational data should also get strong security coverage. Finally, employee and administrator accounts need careful testing as excessive permissions can offer attackers access to multiple systems. Prioritizing such assets can help your organization use security testing services where they matter the most.
Also Read : Why Security Testing Should Be a Top Priority for Insurance Applications?
When Should Businesses Conduct Security Testing?
Security testing shouldn’t be considered a one-time activity performed only after application development. New challenges and risks can emerge as software changes and attackers discover new ways to exploit systems. A proactive testing schedule can help your business identify pain points before they turn into costly security failures. Here are some instances where you need security testing.
➥ Before launching a new application
Every new application should go through rigorous security testing before it becomes available to customers or employees. Launching without a proper assessment can expose your business to risks related to authentication, access controls, and application configurations.
Testing before release can help your development team identify and resolve such weaknesses while changes are still easier and less expensive. It also offers greater confidence that sensitive data and critical functionality are properly protected from the very beginning.
➥ After Major Application Updates
Major application upgrades can unintentionally introduce new security weaknesses. Changes to code, features, and third-party libraries might affect your previously secure functionality. Conducting security testing after major updates can help your business verify that new changes have not created vulnerabilities or weakened existing security controls.
➥ Following Infrastructure or Cloud Migrations
Moving systems to new servers, cloud platforms, and infrastructure environments can create security risks if configurations and access controls are not properly integrated. On the other hand, cloud migrations might introduce issues like excessive permissions and weak identity controls.
Security testing after a migration can help you verify that the new environment is configured safely and the sensitive data remains protected. It also ensures that security controls continue to function efficiently after the infrastructure has gone through certain changes.
➥ After introducing new APIs or Integrations
New APIs and third-party integrations can escalate an organization’s attack surface by generating additional connections between systems. Such integrations might expose sensitive data or introduce weaknesses related to authentication, authorization, and access control. Security testing should be performed whenever your business introduces major APIs or integrations.
➥ Before Compliance Audits
Security testing is also necessary before compliance audits, especially for organizations subject to industry standards and data protection regulations. Conducting assessments in advance can help you identify security gaps that could affect your audit readiness. Working with an experienced QA security testing company can help you assess your applications and infrastructure against relevant security expectations.
➥ After Significant Security Incidents
A security incident should always trigger a detailed assessment of affected systems and controls. Whether the incident includes unauthorized access, data exposure, malware, or an attempted attack, security testing can help you determine how the weakness occurred and whether similar risks exist elsewhere.
➥ At Regular Intervals as Part of Ongoing Security Programs
Security testing should be conducted on a regular basis to know if your product is working in your favor. As systems are changing continuously, new vulnerabilities are discovered, and your secure applications might be exposed over time. Regular assessment, penetration testing, and targeted security reviews can help your business maintain visibility into the changing risk landscape.
Ready to Identify the Right Security Testing Strategy?
Choosing the right security testing strategy starts with assessing your business and the elements that make it vulnerable. So, make sure you understand your recent security risks and review the applications and systems your company mainly relies on. Further, identify the testing approaches that can address your actual attack surface. Instead of treating every risk equally, prioritize issues as per their seriousness and how they can impact the whole infrastructure.
A structured approach can help your business invest in the security assessment that you genuinely need while prioritizing resources on critical risks. Working with an experienced security QA testing company can also offer access to the expertise needed to evaluate complicated applications and security controls.
You shouldn’t limit yourself to finding vulnerabilities only. It is all about understanding which risks matter the most and resolving them before they can challenge your business and might compromise your sensitive data.